Gatekeeper flow: from a tested policy to a decision and an audit report

Scroll or pinch to zoom, drag to move, double-click to zoom in 100% SVG PNG Back to the post
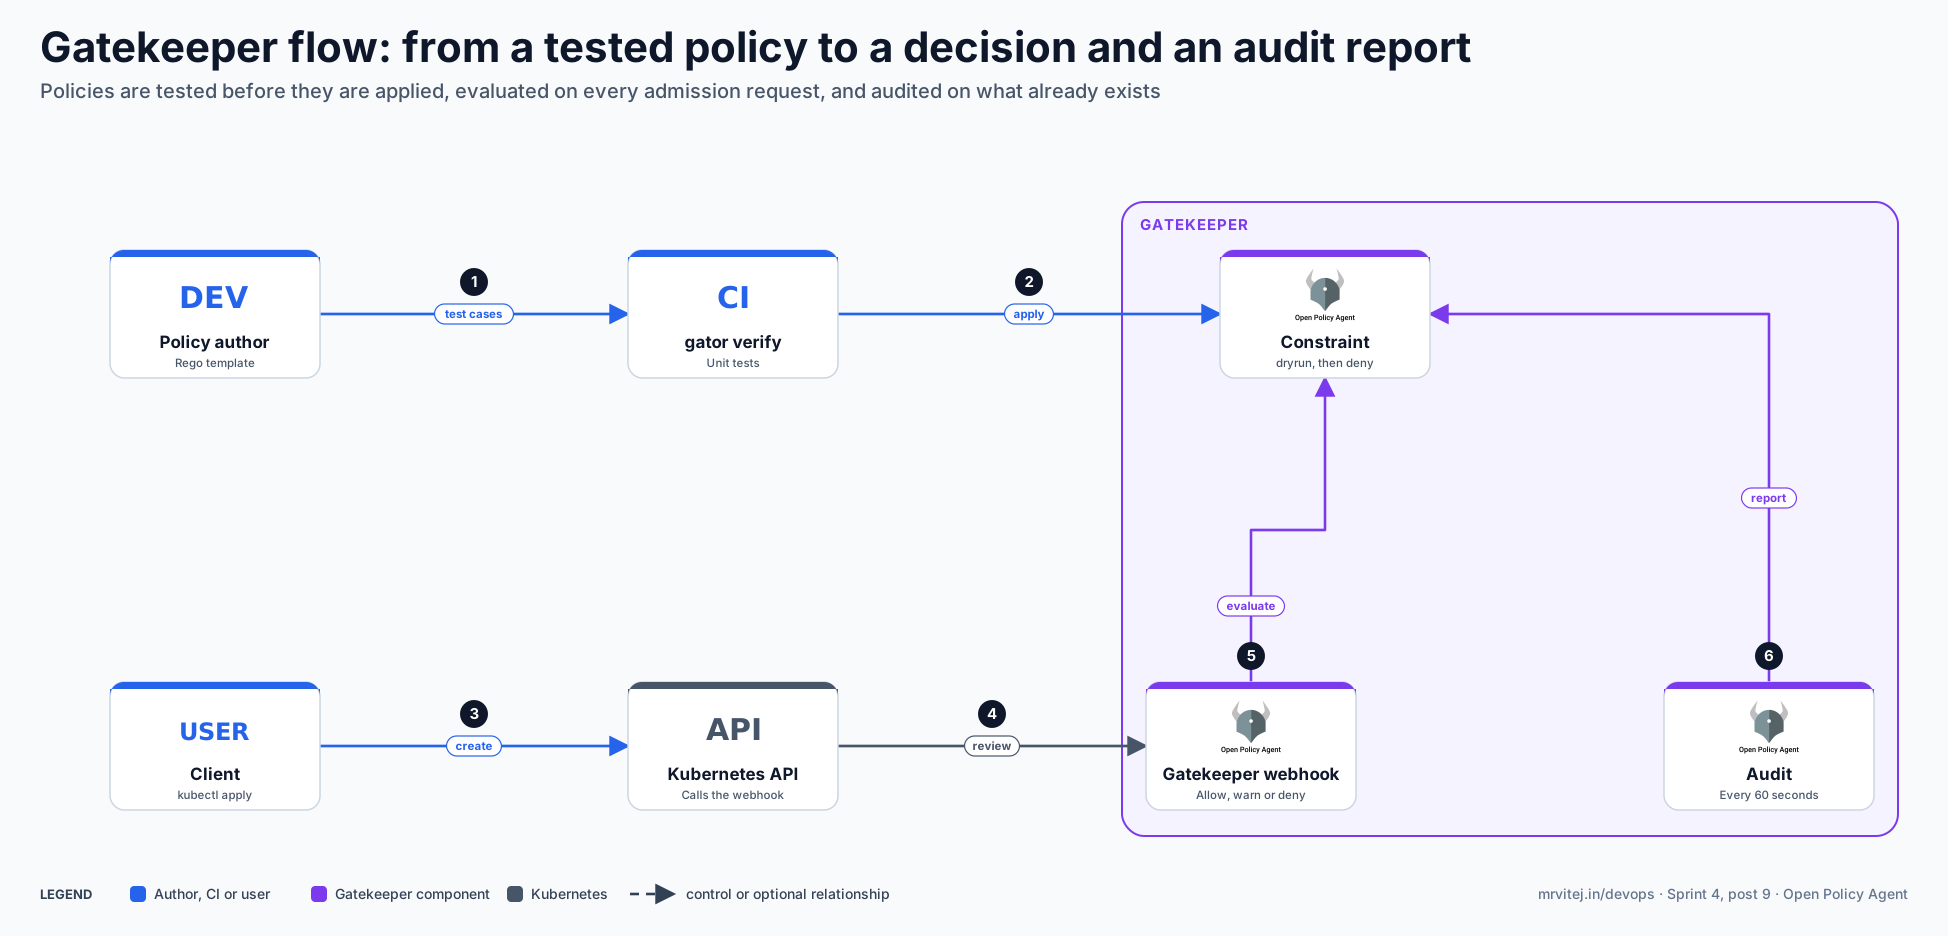
Gatekeeper flow in six steps: the policy author writes test cases and runs gator verify; the policy is applied as a constraint, first in dry-run; a client creates a resource; the Kubernetes API calls the Gatekeeper webhook with an admission review; the webhook evaluates the request against the constraints and allows, warns or denies; the audit component evaluates existing resources against the same constraints and records violations.